Cybersecurity answers you can check
Lattice is a read-only graph of public cybersecurity knowledge: CVEs, CISA’s exploited list, ATT&CK techniques, weaknesses and detection rules, cross-linked. The difference from a search tool is on every link: whether a source stated it, or we inferred it. Use it from a chat, from your AI agent, from the command line or from a desk of notes.
Four ways in
SOC and IT security teams
Lattice Analyst
Paste an alert, an email, logs or CVE ids, or ask about one.
It answers with a label, the reasons, the techniques the text shows and what to check next, and a person decides. A query plan lists every call it made.
Open the AnalystAI agents and the people who build them
Lattice MCP
Seven read-only tools over the graph, for Claude, Cursor and any MCP client.
Look up an id, follow the links and report where each came from. Looking up an id and reading a node need no key.
Connect an agentIT admins and security engineers
lattice-scan
Compare this machine, or a project folder, with what CISA lists as exploited.
Open source command line tool and a Claude skill. Each match is a candidate for you to check. Only CVE ids leave the machine.
Which way in fits your jobAnyone who needs one CVE, today
Triage desk
Search every note by CVE, product, weakness or technique.
Our technical analyses of exploited CVEs, with CISA's deadline. For an id with no note, the record the graph holds.
Open the Triage deskThe Lattice Analyst: an assistant that shows its work
Facts, labels and structure are written in code from the graph. A local language model words the explanation, and the answer is checked against the evidence before you see it. It gives a label with the reasons so you can act or escalate, and it never says “safe”. Each answer lists what is missing, and containment steps are suggestions for a person to approve.
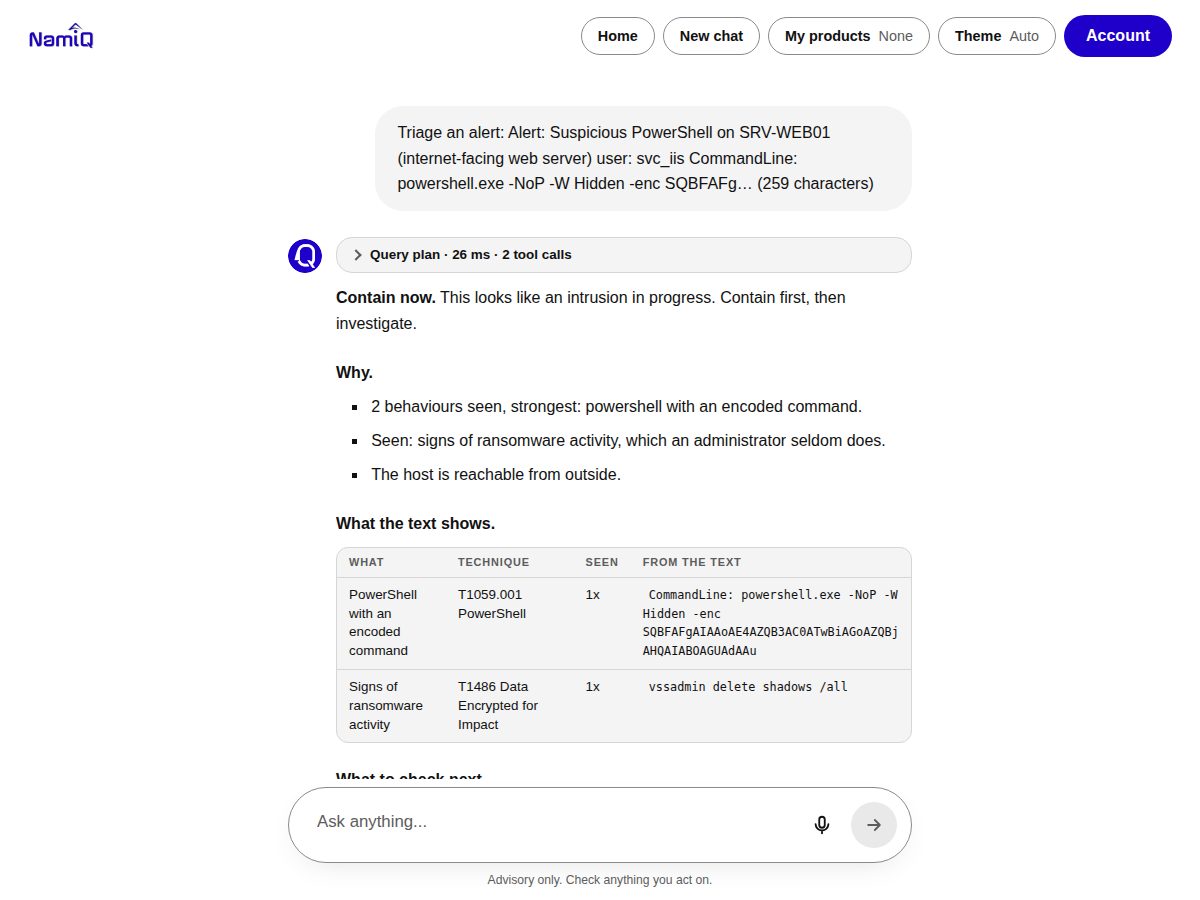
The tasks an analyst repeats every day
- Triage. Today's briefing · Triage an alert · Triage an email · Triage scanner output
- Investigate. Build a timeline from logs · Investigation checklist · Hunt hypotheses · What usually follows
- Respond. Draft the messages · Containment plan · Ask the runbook · Which CVEs to patch first
- Improve. Post-incident report · Draft a detection rule
- Personal. Save the products you run in your browser, then ask whether a CVE affects them.
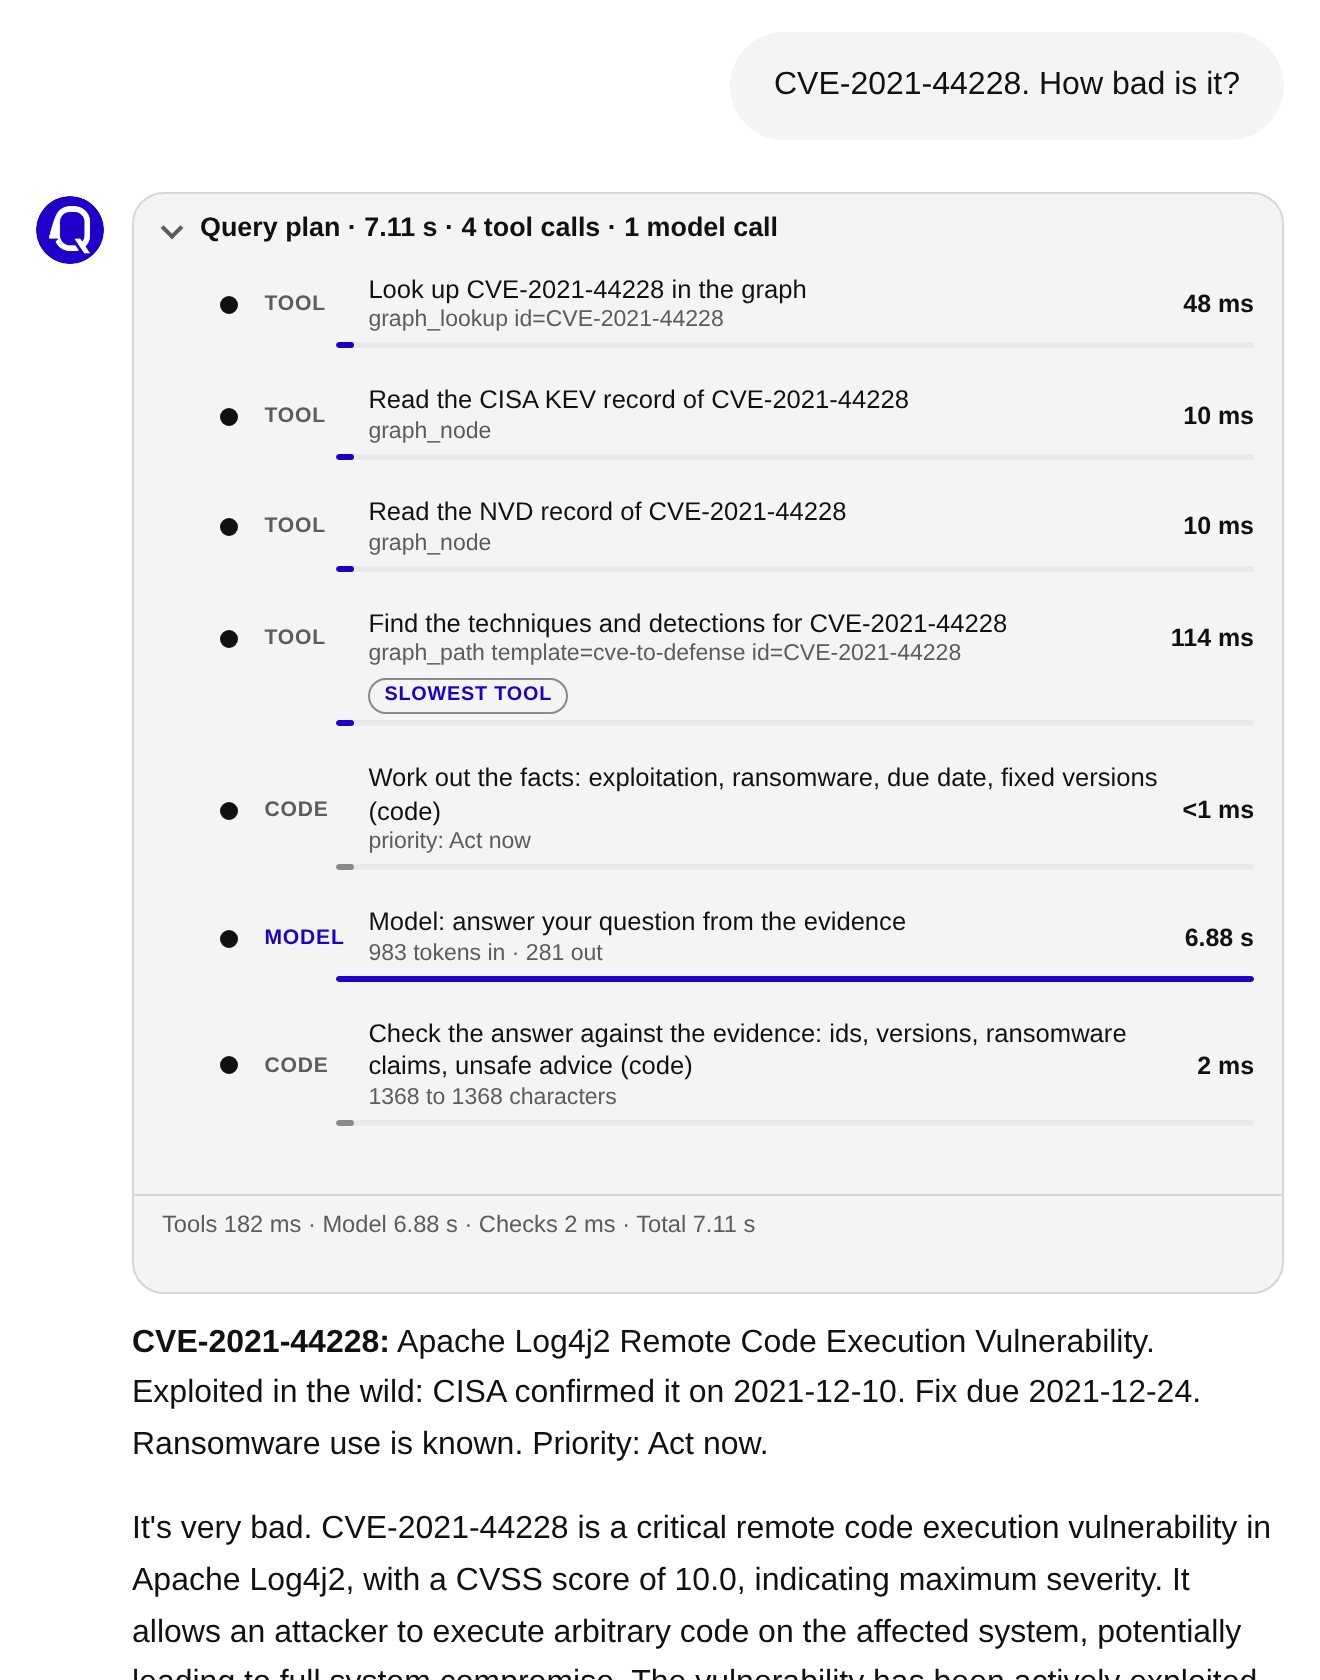
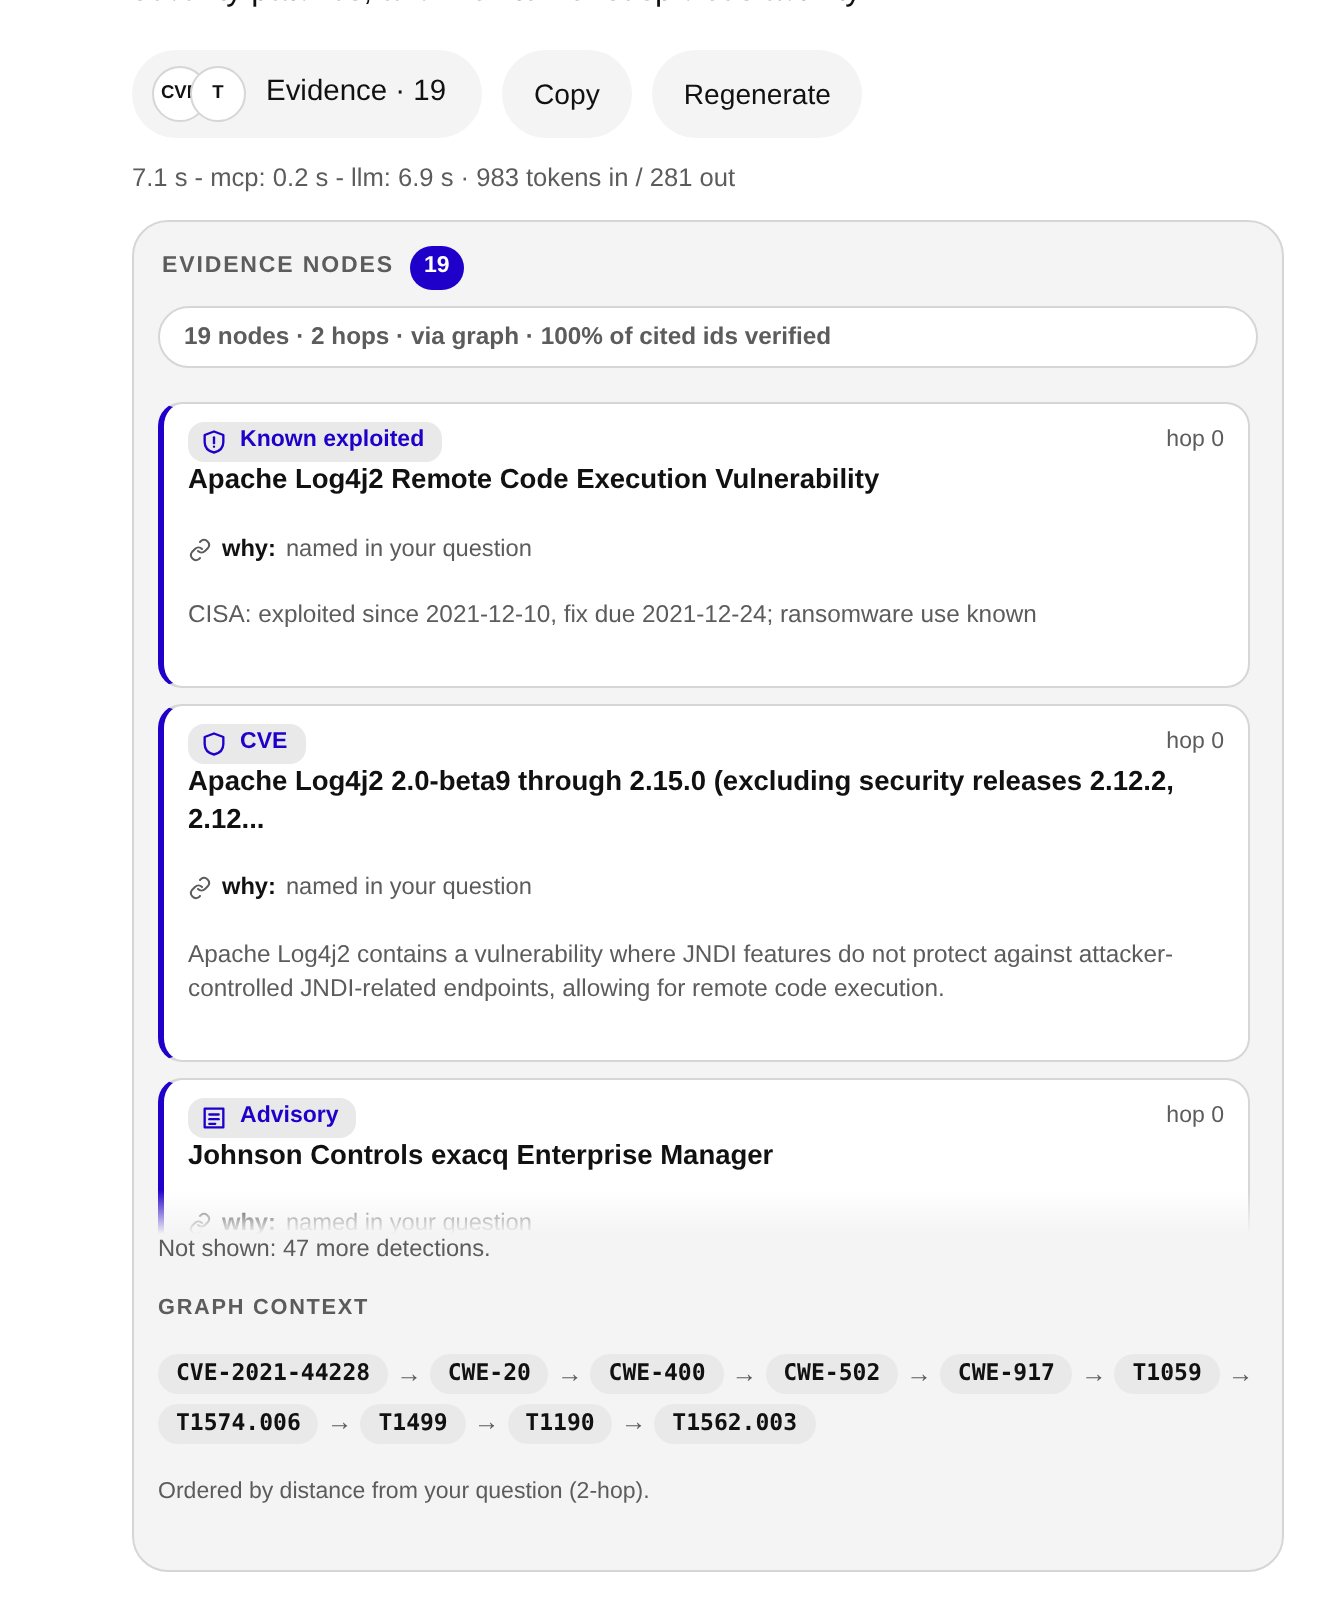
It does not connect to your SIEM or scan your network. It works on what you paste and on public data, so it cannot tell you whether you are affected, exploited or covered by a rule. Open it on a phone or a desk; it follows the light or dark theme and can be installed as an app. Open the Lattice Analyst.
lattice-scan: check a host or a project
Apache-2.0licensed command line tool. It reads CISA’s exploited list through Lattice and compares it with the packages, containers, hardware and kernel of the machine it runs on, or with the dependencies a project folder declares. It prints evidence for you to read, and each match is a candidate, not a finding that anything is vulnerable. lattice-scan posture adds what the host exposes and runs. Only CVE ids leave the machine; the inventory is never sent.
pip install lattice-scan
lattice-scan                       # today's exploited list against this machine
lattice-scan --cve CVE-2021-44228  # one CVE
The Claude Code skill runs the same check from a chat on the machine Claude runs on (/plugin marketplace add namiq-ai/lattice-scan). A signed apt repository is at the connection guide; the code is at GitHub. The licence covers the tool, not the Lattice service or the data behind it.
Guides by role
AI agents and the people who build them
An agent that says "likely" instead of "is".
Every link carries a source, a confidence figure and a basis, so your agent can report what a source stated and what was inferred. Discovery needs no key.
Teach your agent to say likelySOC analysts
Four questions for any new CVE.
Which techniques are associated with it, who said so, which detections exist, and what the graph does not know. The gaps are part of the answer.
A CVE, an agent, and four questionsCIOs and security leaders
Five questions before an agent relies on security reference data.
Your people may already ask assistants about CVEs. The questions apply to any vendor, and the guide answers each one for Lattice, including the parts that are not flattering.
Five questions to ask firstWhat an answer looks like
- Every link says where it came from. A source stated it, or we inferred it, and inferred links carry a confidence figure so the agent can say “likely” and not “is”.
- Gaps are reported as gaps. If a step has no data, the answer says so instead of filling it in.
- Licence notices travel with the data. Each answer names the sources whose attribution you must keep.
- Only public identifiers go in. The interface takes CVE numbers, ATT&CK ids and the like, and rejects free text, so there is nowhere to put your own data.
How it fits with what we already do
Lattice is reference knowledge. It does not look at your systems. These are the pieces that do, and the reading that goes with them.
- IT and security for small firms — The service: someone who looks after your own estate.
- The IT check — Where your own estate stands today. Reference knowledge is only useful read against something real.
- OCO — The cyber graph behind this. Lattice serves public knowledge; OCO is the product that works on an estate.
- Monthly highlight — The month's changes in the exploited list, for a security leader.
- Security questionnaires — AI use can be a line on those. The CIO guide helps you answer it.
What it is not
It does not look at your systems, find anything in them, or tell you what to fix. It is reference material, it can be wrong or out of date, and inferred links are guesses. It is a test of an unfinished service: it comes as is, with no warranty, no uptime promise and no promise it will continue. Read the beta terms before you ask.
Guides
- A new CVE, an agent, and four questions — For SOC analysts, 5 minute read.
- Five questions to ask before an AI agent relies on security reference data — For CIOs and security leaders, 6 minute read.
- Teach your agent to say "likely" and not "is" — For agents and the people who build them, 4 minute read.
- Connection guide — the commands for Claude Code, Claude Desktop, Cursor and plain HTTP.
Reference for the Lattice MCP cybersecurity server
Which way in fits your job, the tools and their exact arguments, how to connect each client, and when a graph is the wrong choice.
- Check what you run against today's exploited list, in the chat — 4 minute read.
- Skill, command line or MCP: which way into Lattice, and how to use it — 7 minute read.
- The seven Lattice tools and their exact arguments — 4 minute read.
- Connect Lattice to Claude Code — 2 minute read.
- Connect Lattice to Cursor or Claude Desktop — 2 minute read.
- Connect Lattice to claude.ai — 2 minute read.
- A model's memory, a document search or a graph: which one should your agent ask? — 4 minute read.
Get a trial key
Trial keys are issued automatically to the email address you give, with the server address. They have usage limits, expire, and can be withdrawn at any time. When you reach a limit you can verify your account to triple it. For unlimited or commercial use, contact [email protected].